

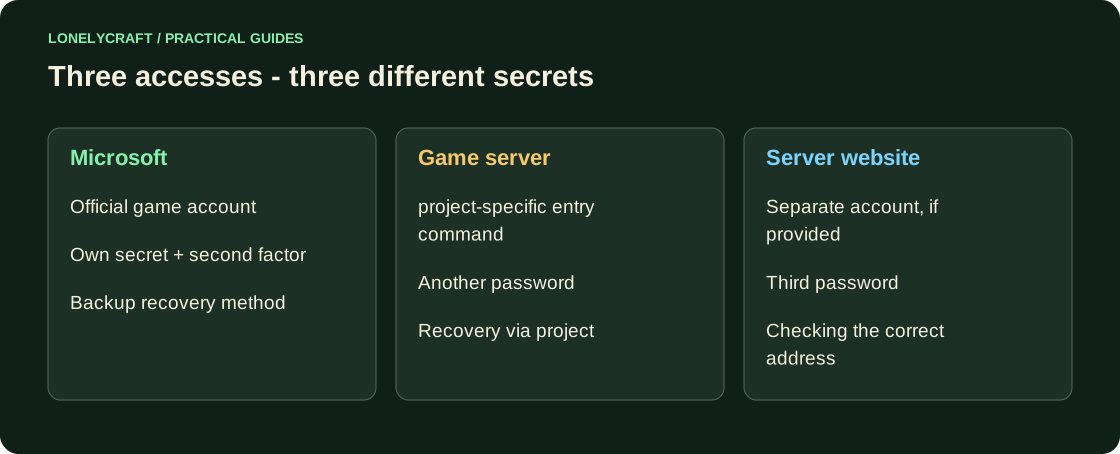
Do not enter the same password into different systems
The Microsoft password confirms access to the official account. The server command /login is specific to the server's system and should not receive your Microsoft or email password. If a site uses a separate registration, it also needs its own password.
A password manager helps you store various long secrets. Open the server and website address from the saved entry, and not from the “urgently confirm rank” link in a personal message. For an official login, check the page domain before entering your details.
Protect your Microsoft account and recovery methods
Open Microsoft Account Security yourself. Check your login methods and up-to-date recovery data, then set up two-step verification using official instructions. The names of the buttons and the methods offered depend on the account.
Store the recovery code separately from the device you use as a second factor. Make sure a recovery method will still be accessible if your only phone is lost. Never send a verification code or 2FA setup QR to a “support employee”: they can use it to gain access.
Mods and launchers execute code
JAR mod is an executable program. Download the file from the author's page, check the game, loader and dependencies. A separate profile separates mods and saves, but is not a security sandbox for malicious code.
Be wary if they offer to run an unknown EXE, disable protection, or insert a PowerShell command for the sake of texture. For modpack, use the manifest provided by the author and the supported installer. A copy of world helps restore data, but does not prevent the malware from gaining access to the device.
Check origins and dependencies before first launch. Fabric installation.
If your credentials may have leaked
From a clean, trusted device, open the official security section, change compromised secrets, and check recent logins and recovery methods. Perform accessible revocation of sessions and permissions of suspicious applications. If the same password was used somewhere else, change it there too.
For a server account, use the official project recovery channel, provide the nickname and time without sending the password. Save the suspicious message and page address. If you launched an unknown file, first deal with the device: changing the password on a still infected system may reveal it again.
Keep a list of installed files and author pages to understand the latest changes. Checking the composition of the assembly.
